This site is still being built · Live now (Beta)
isitphish.ai/examples

Examples

Two real emails we tested. What you see is what isitphish actually produced, with one made-up row added to show a redirect (marked below). We removed names, email addresses, IP addresses and tracking codes, and every web address is written in a broken-up form (hxxps, [.]) so it cannot be clicked.

Example 1  The "Netflix" payment emailCase TCF-2026-C9A37

It said Netflix. It wasn't.

An email titled "Your Netflix Membership Has Ended - Renew to Continue" asked for a payment. isitphish read it and found:

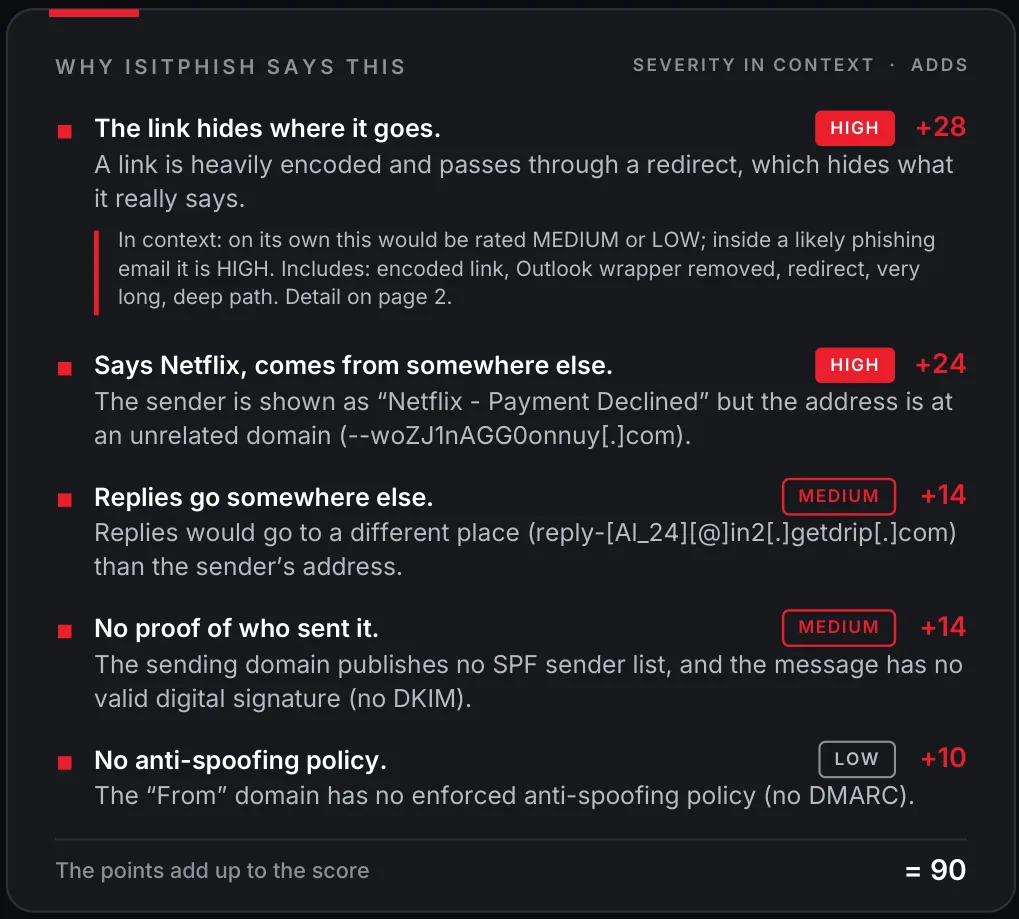
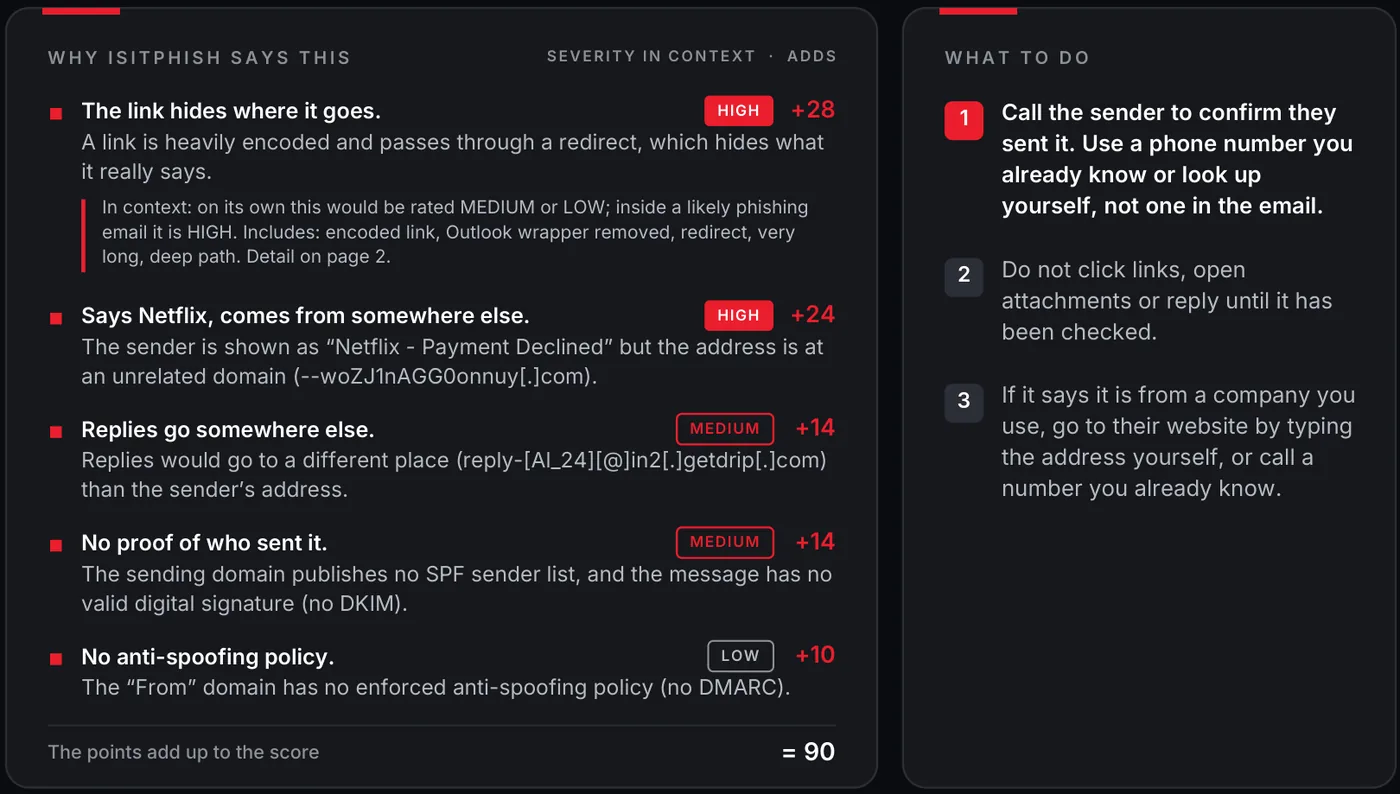
  • 1The sender's name says Netflix, but the address is a different web domain: --woZJ1nAGG0onnuy[.]com.
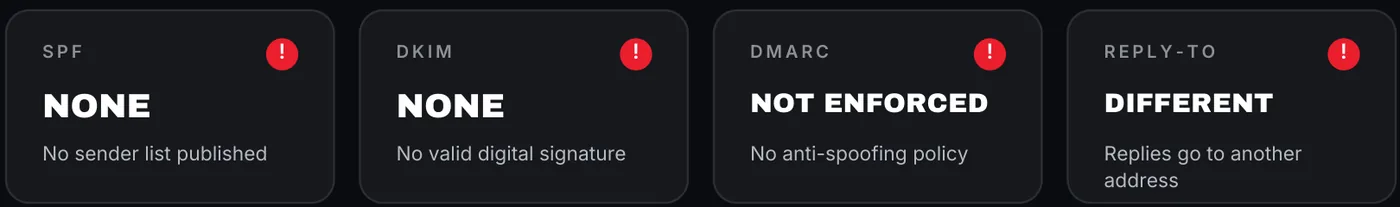
  • 2Replies would go to a different address than the sender's.
  • 3No proof of who sent it: no SPF, no DKIM, no DMARC.
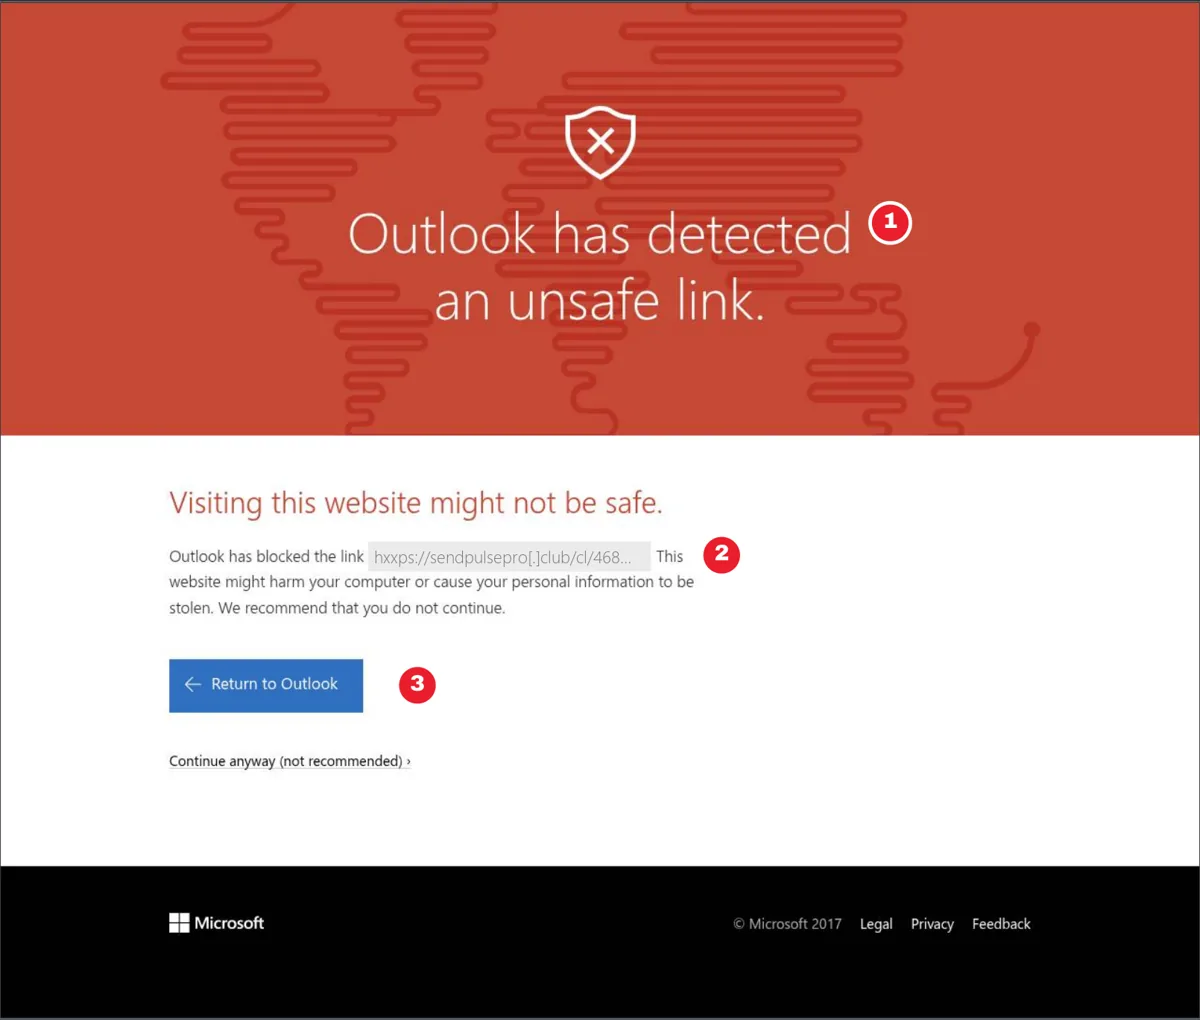
  • 4The link was hidden inside an Outlook link wrapper that points to sendpulsepro[.]club.
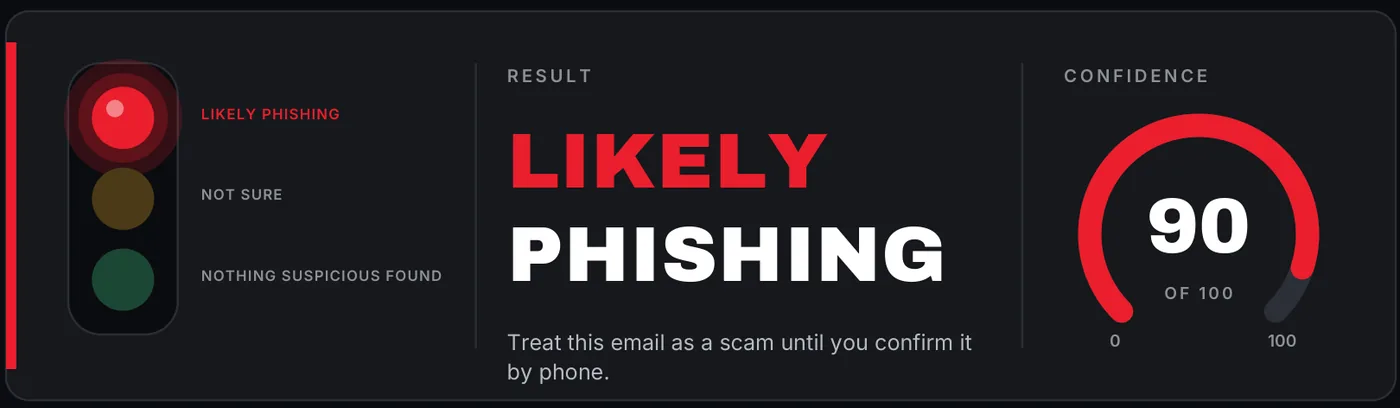
Likely phishingCONFIDENCE 90 OUT OF 100
What our isolated browser sawNo visit needed
Screenshot of the page the link opened

A picture of the page the link opened. The words on it are the page's own, not isitphish's.
The verdict from the reportReal output
Verdict: likely phishing, confidence 90
SPF none, DKIM none, DMARC not enforced, reply-to different
The why in plain EnglishReal output
Reasons and what to doReasons
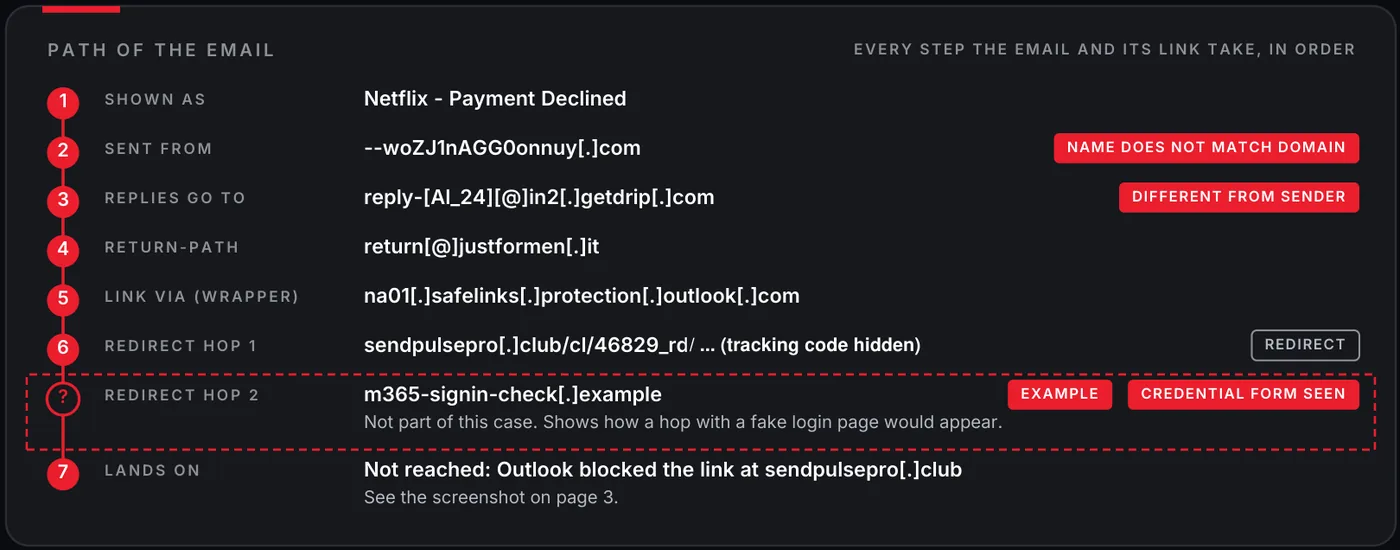
The path the email and link tookReal report + 1 made-up example row
Path of the email
Shown asNetflix - Payment Declined
Sent from--woZJ1nAGG0onnuy[.]com
Replies go toreply-[AI_24][@]in2[.]getdrip[.]com
Link viaOutlook wrapper
Redirectsendpulsepro[.]club (tracking code hidden)
Lands onNot reached: Outlook blocked the link

The dashed row marked EXAMPLE ("Redirect hop 2") is not part of this email. It shows how a step with a fake login page would appear.

De-identified: recipient details, IP addresses and tracking codes removed; addresses defanged. Verdict shown is the report's own. The pictures are taken from the PDF report: where they say "page 2" or "page 3", they mean pages of that report.
Example 2  A second phishing email we testedLink check

Different email, same trick.

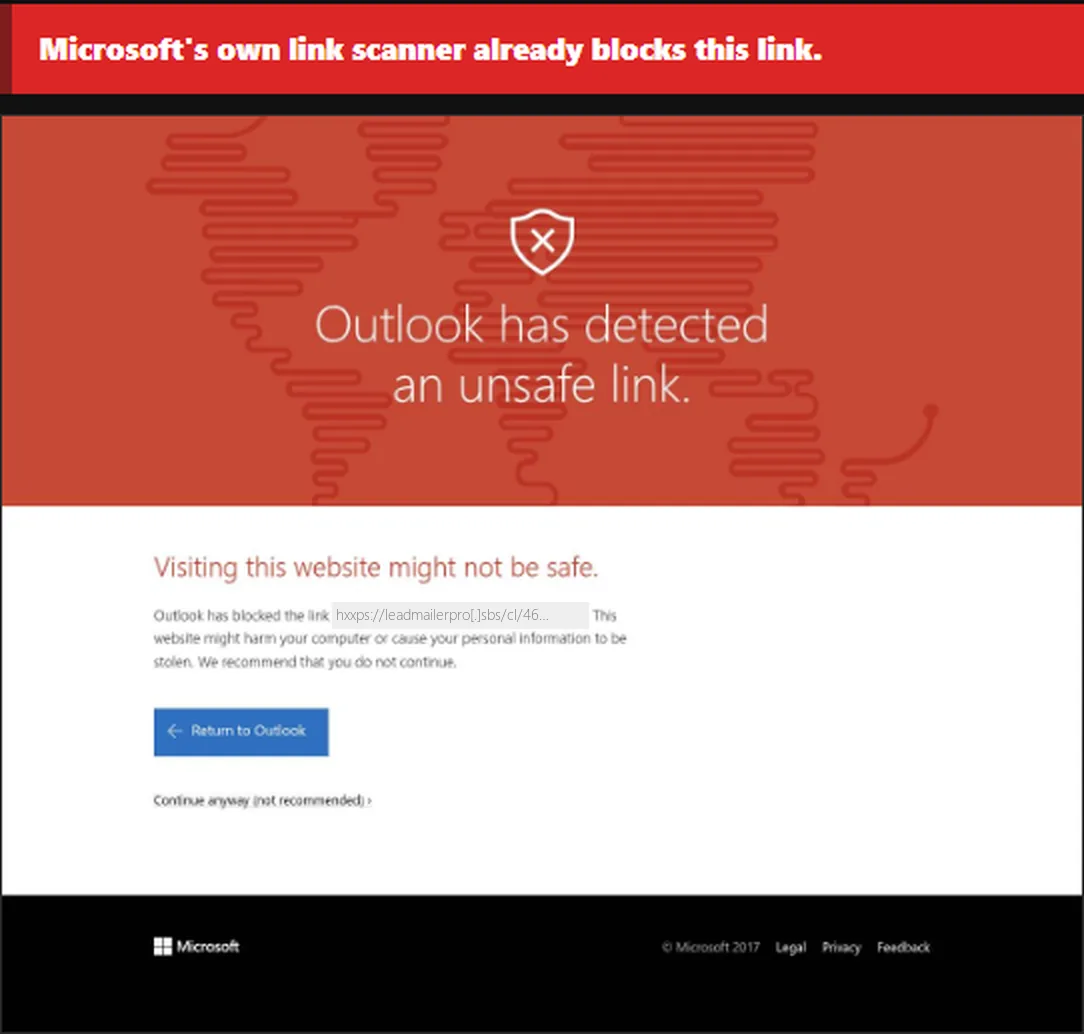
This one hid its link inside an Outlook link wrapper too. Behind the wrapper was leadmailerpro[.]sbs.

  • 1isitphish read the link: an Outlook address with leadmailerpro[.]sbs behind it.
  • 2Our isolated browser opened it and took the picture on the right.
  • 3Outlook's own link scanner already blocks this link, so isitphish says so on the result.

Even when a scanner has blocked a link, you still get to see why it was a problem, and you still call the sender before you act.

Result card from isitphishReal output
Result: Microsoft's own link scanner already blocks this link, with the screenshot

The words on the page are the page's own, not isitphish's. The link address is defanged here.
The
rule

Call the sender to confirm. Use a phone number you already know or look up yourself, not one in the email.That is advice number one, whatever any checker says, including ours.

Got one like these?

Try a free check now, or see the plans.