A phishing email only has to fool you once. isitphish looks at the four places it usually gives itself away, then explains what it found.
The name you see against the address it truly came from, where replies go, and whether the sender can be verified.
We unwrap redirects and wrapper addresses to show where a link actually lands.
Names and web addresses dressed up to pass for a company you know, when they are not.
We open the link in an isolated browser and take a picture, so you never have to visit it yourself.
Copy the email, or choose a saved .eml file, and drop it in the box.
We check the sender, the links and the look-alikes, and can take a picture of where the link lands.
A traffic light, the reasons in everyday words and a short report. Then you call the sender.
A traffic light and how sure we are, so you can see the answer in one look.
Short reasons, no jargon, that you can read out to a coworker.
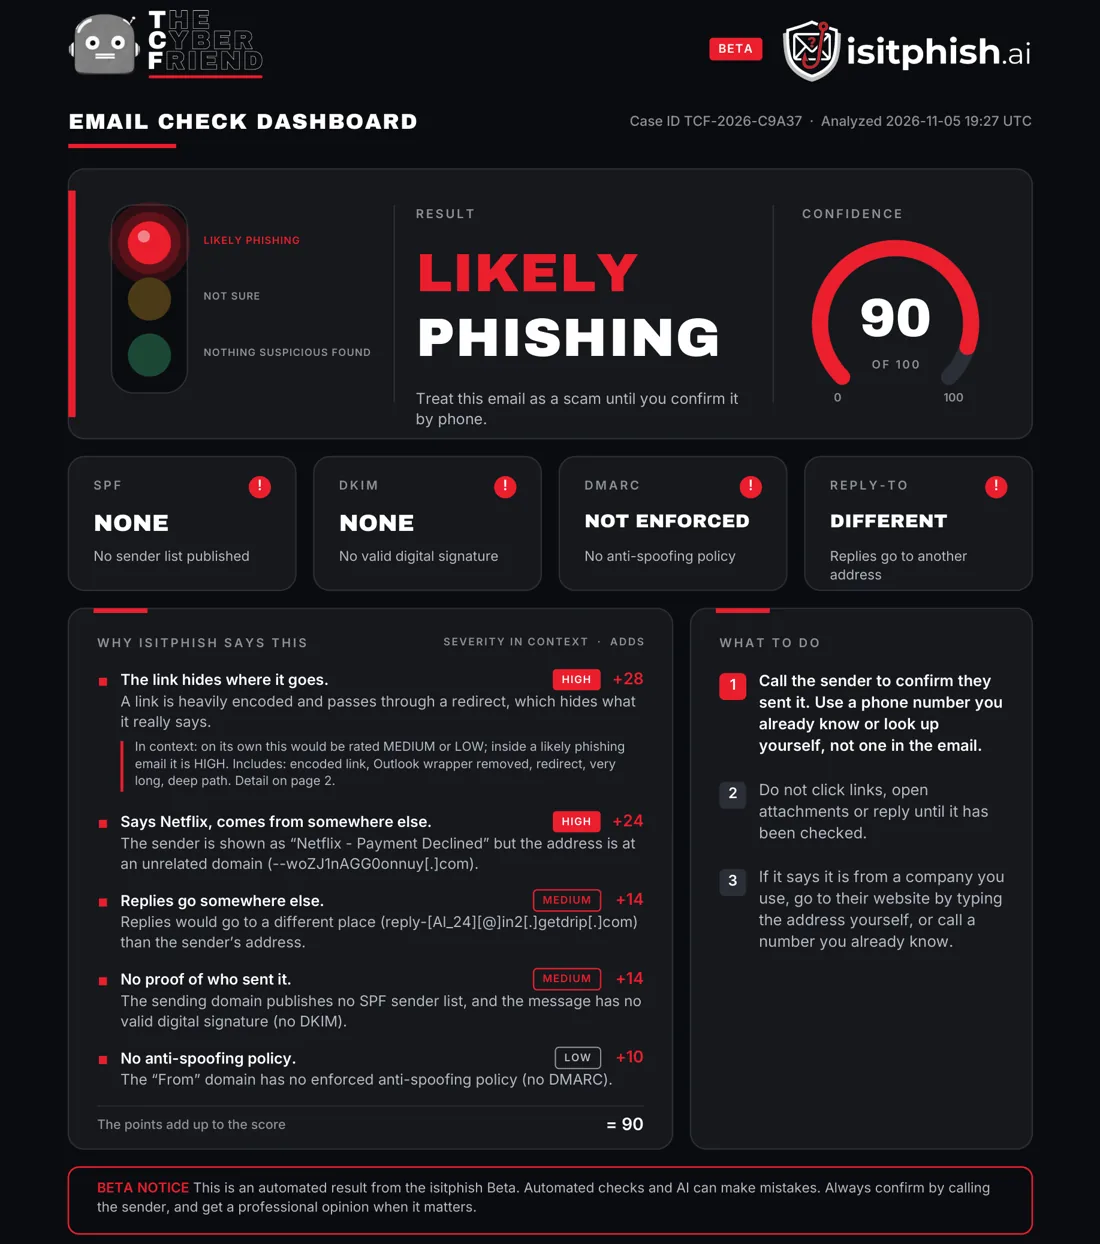
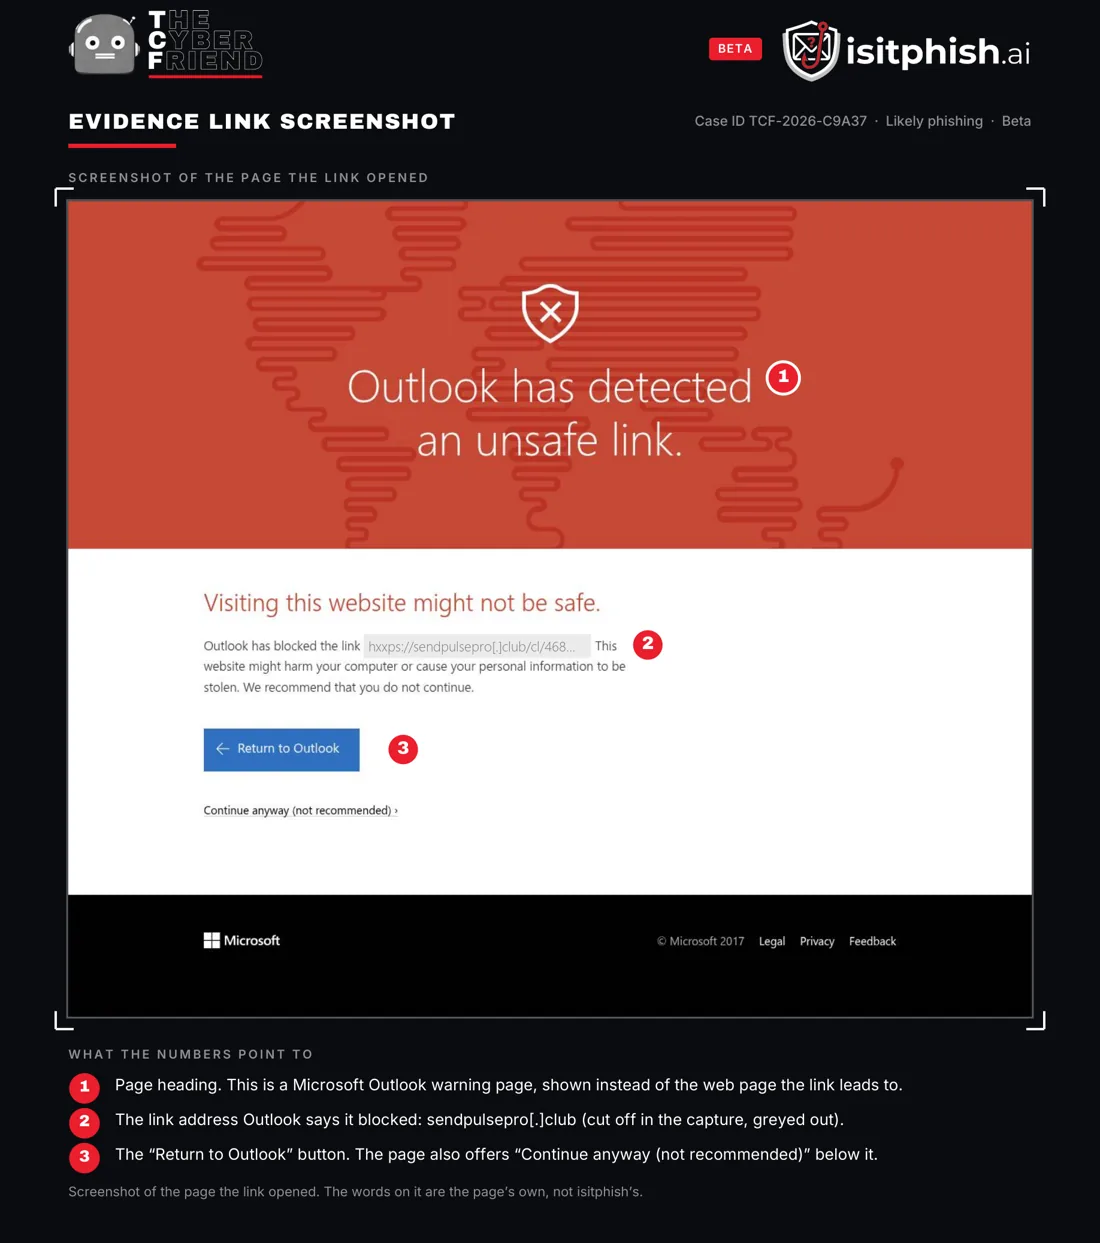
A short PDF of everything we found, to keep or to hand to whoever looks after your IT.
Call the sender to confirm. Use a phone number you already know or look up yourself, not one in the email.That is advice number one, whatever any checker says, including ours.
See the plans, or try a free check now.